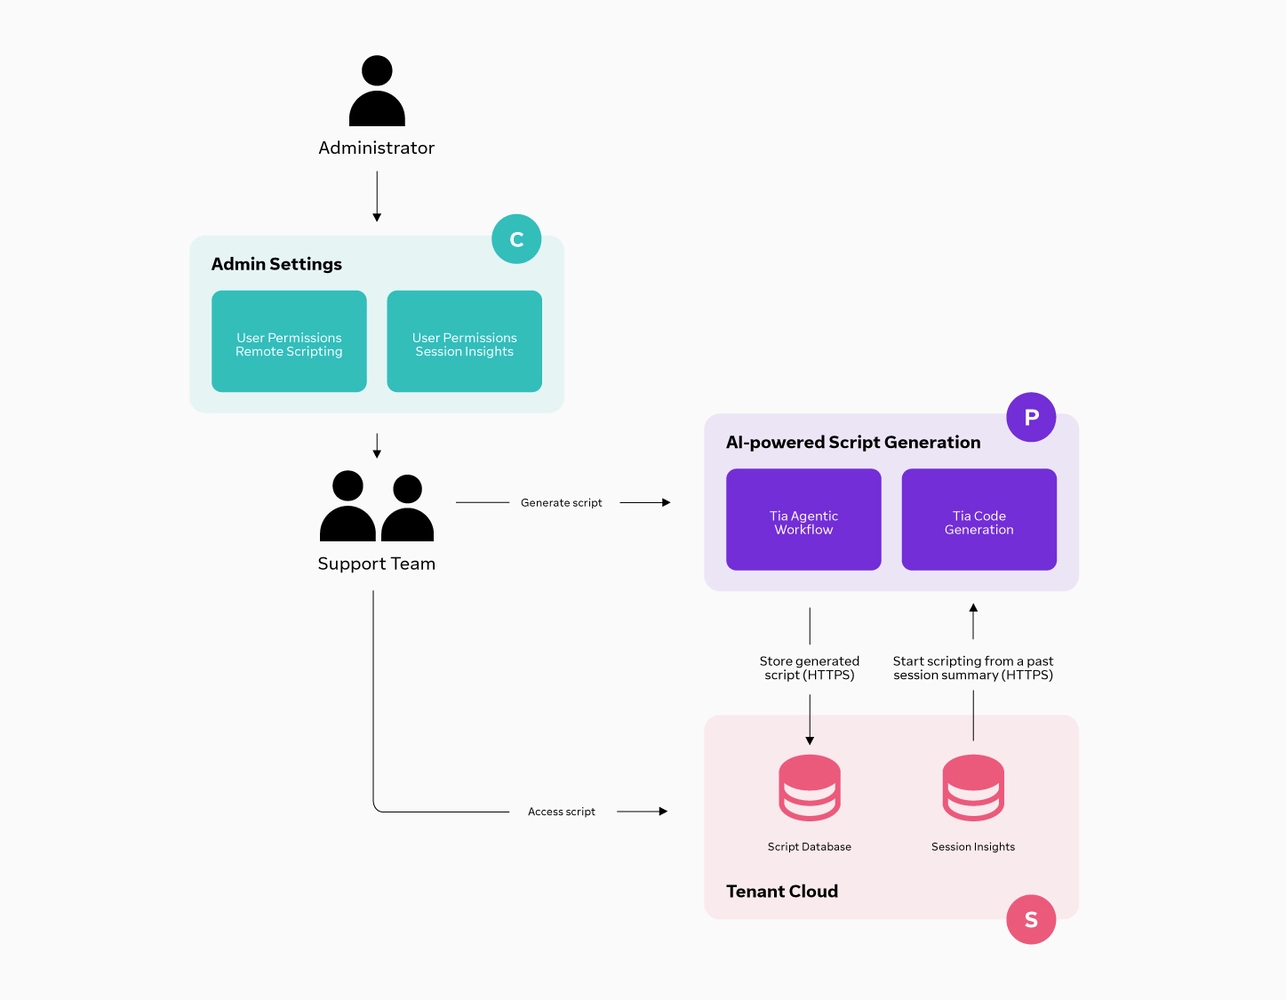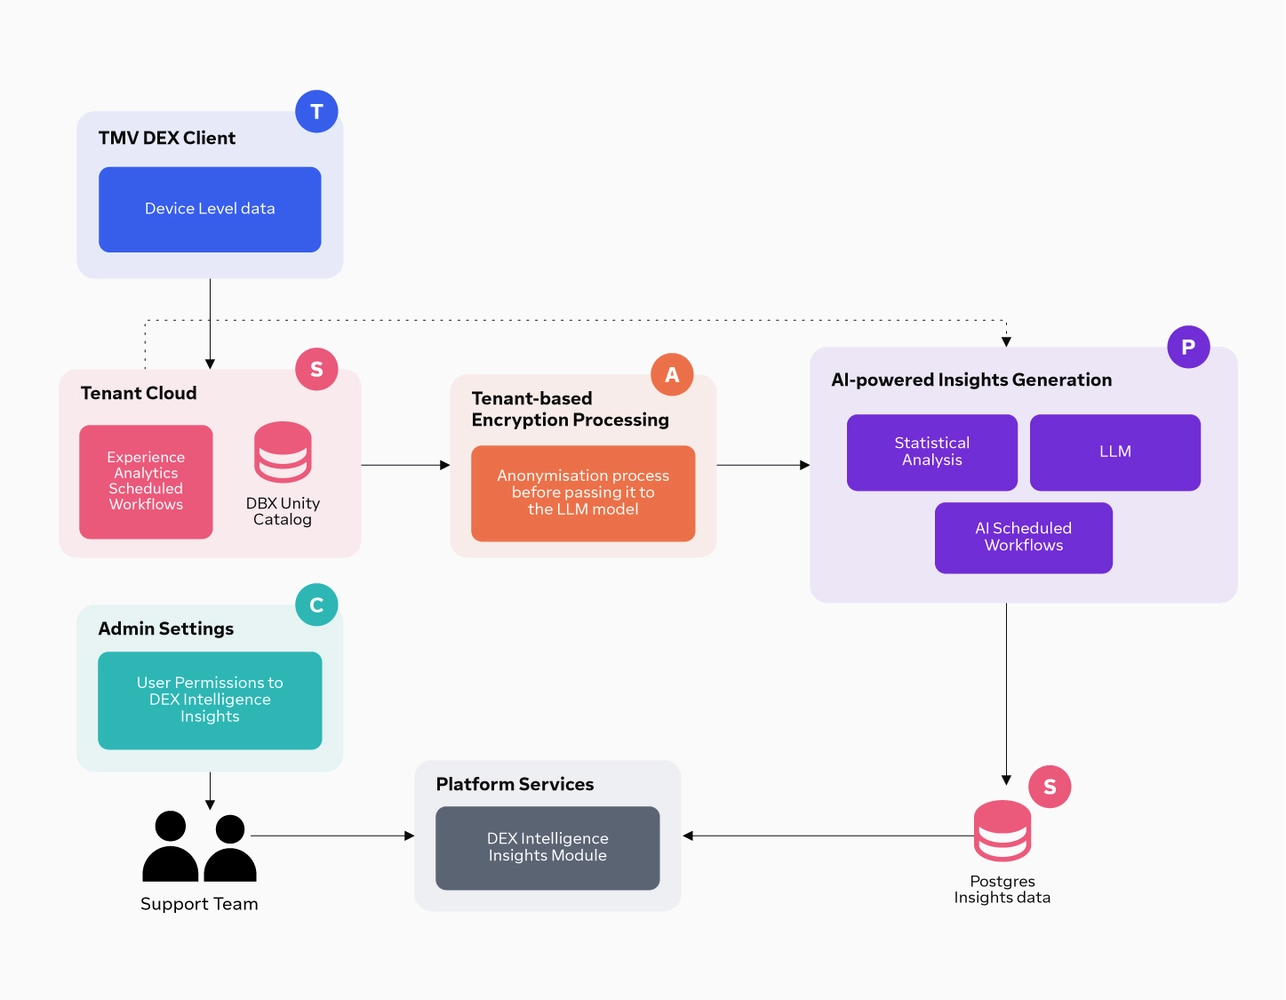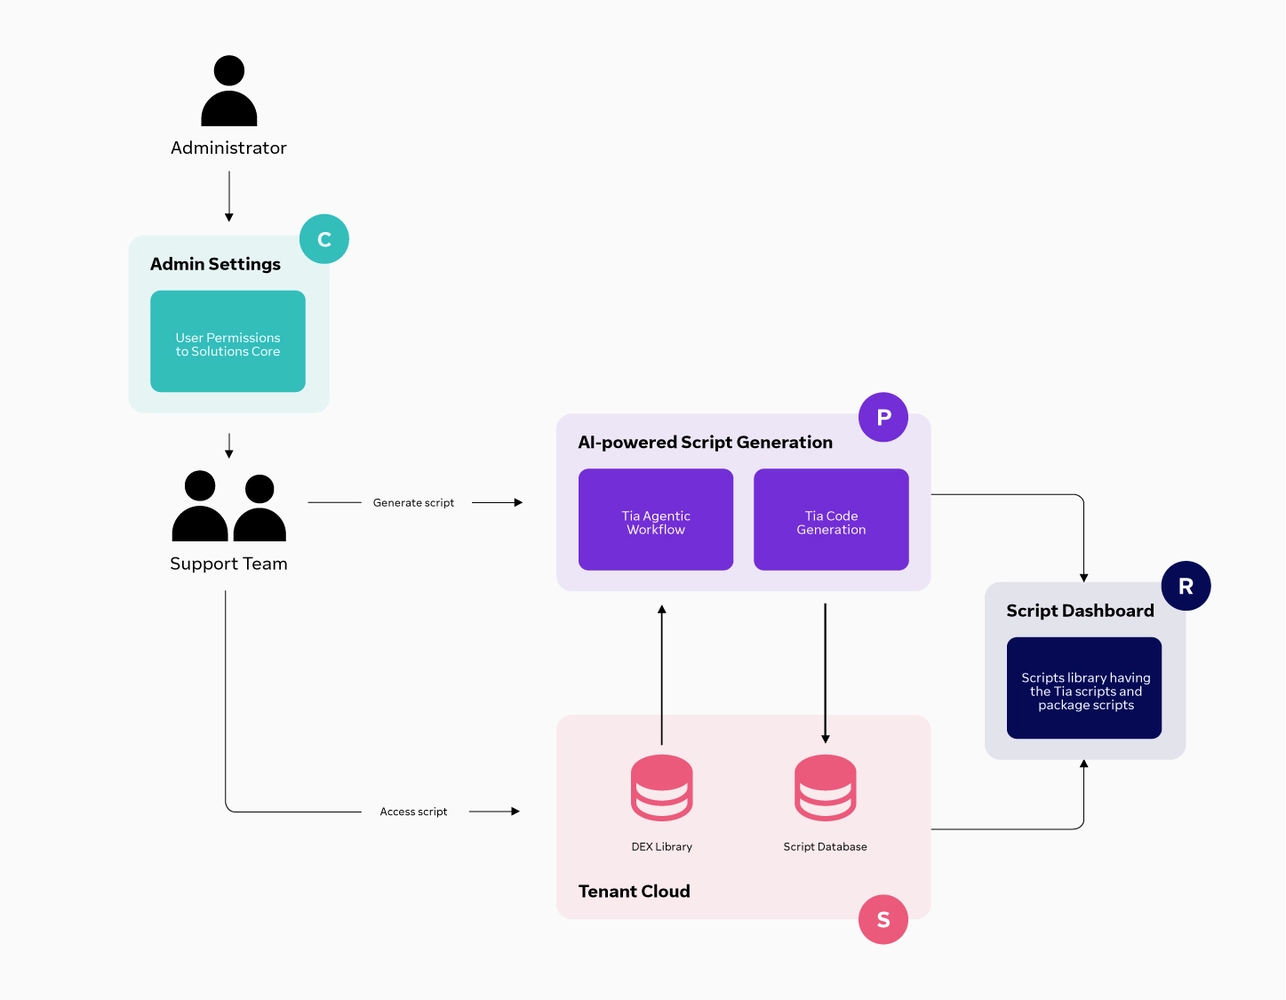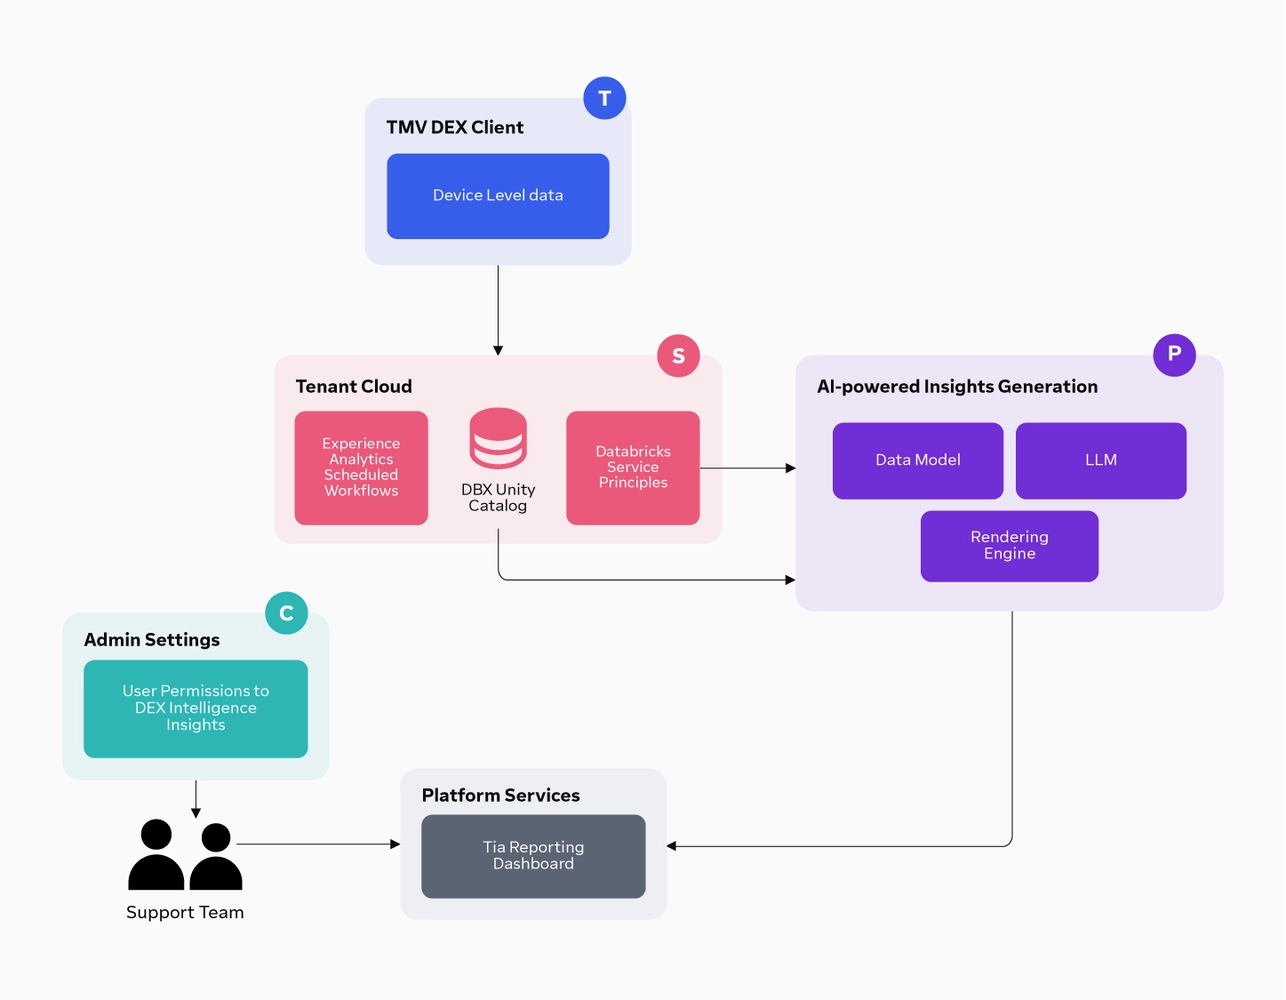


SESSION INSIGHTSSession documentation
Session documentation protected with client-side encryption
- Session data is anonymized on the client before leaving the endpoint (rule-based masking).
- Session data is protected using client-side encryption (CSE).
- The public key is obtained over HTTPS, and the private key is protected and unwrapped in a certified HSM with audited operations.
- Additional anonymization is applied through cloud-based services (non-public details available under NDA).
- Data is encrypted in transit (HTTPS/TLS) and at rest (AES-256).
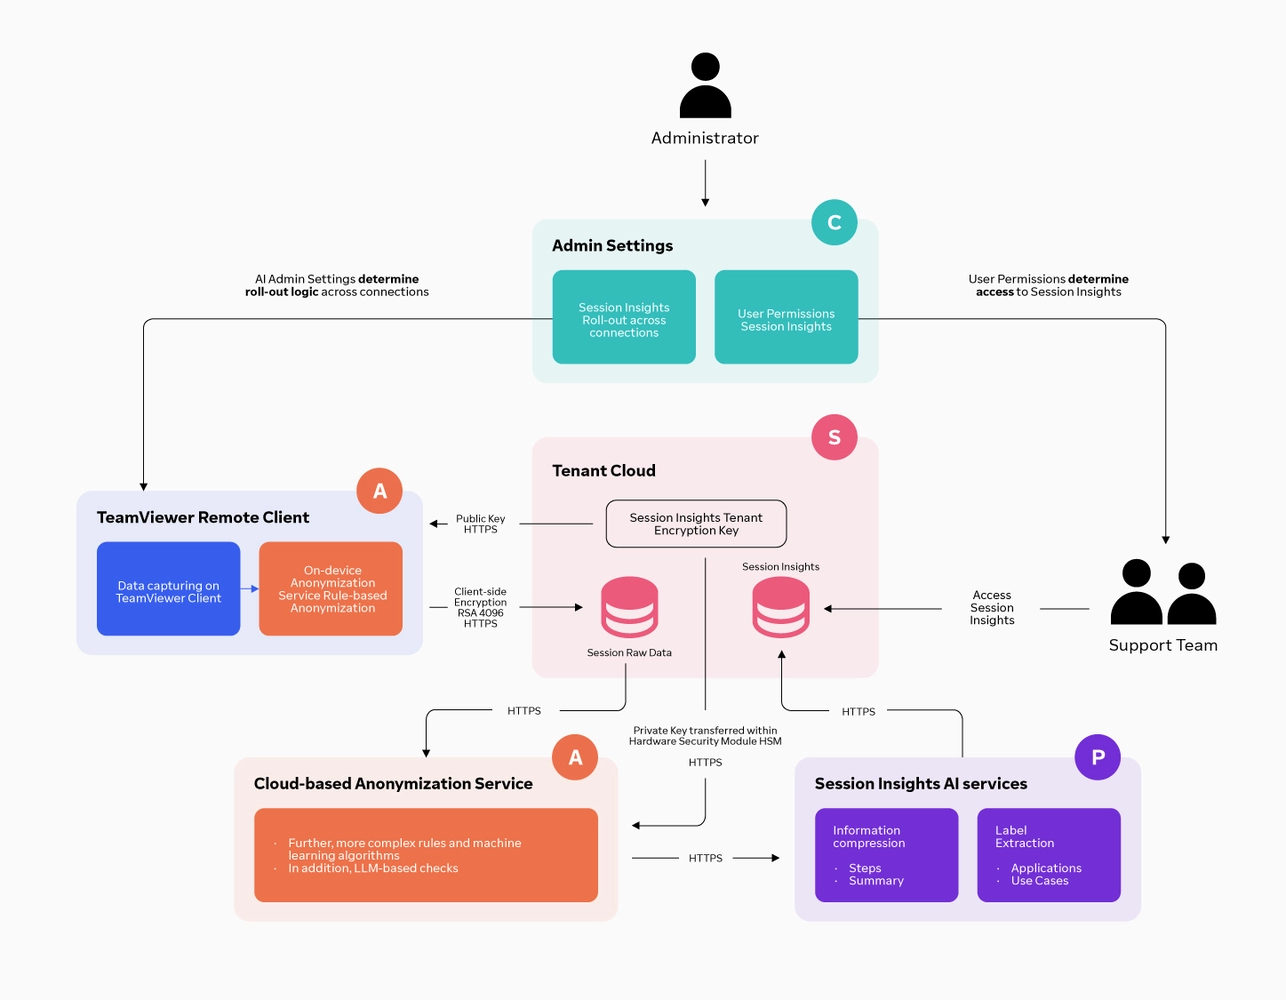
Policy-controlled session summaries, protected end to end with anonymization and encryption.
(Click image to enlarge)